Privacy Impact Assessment
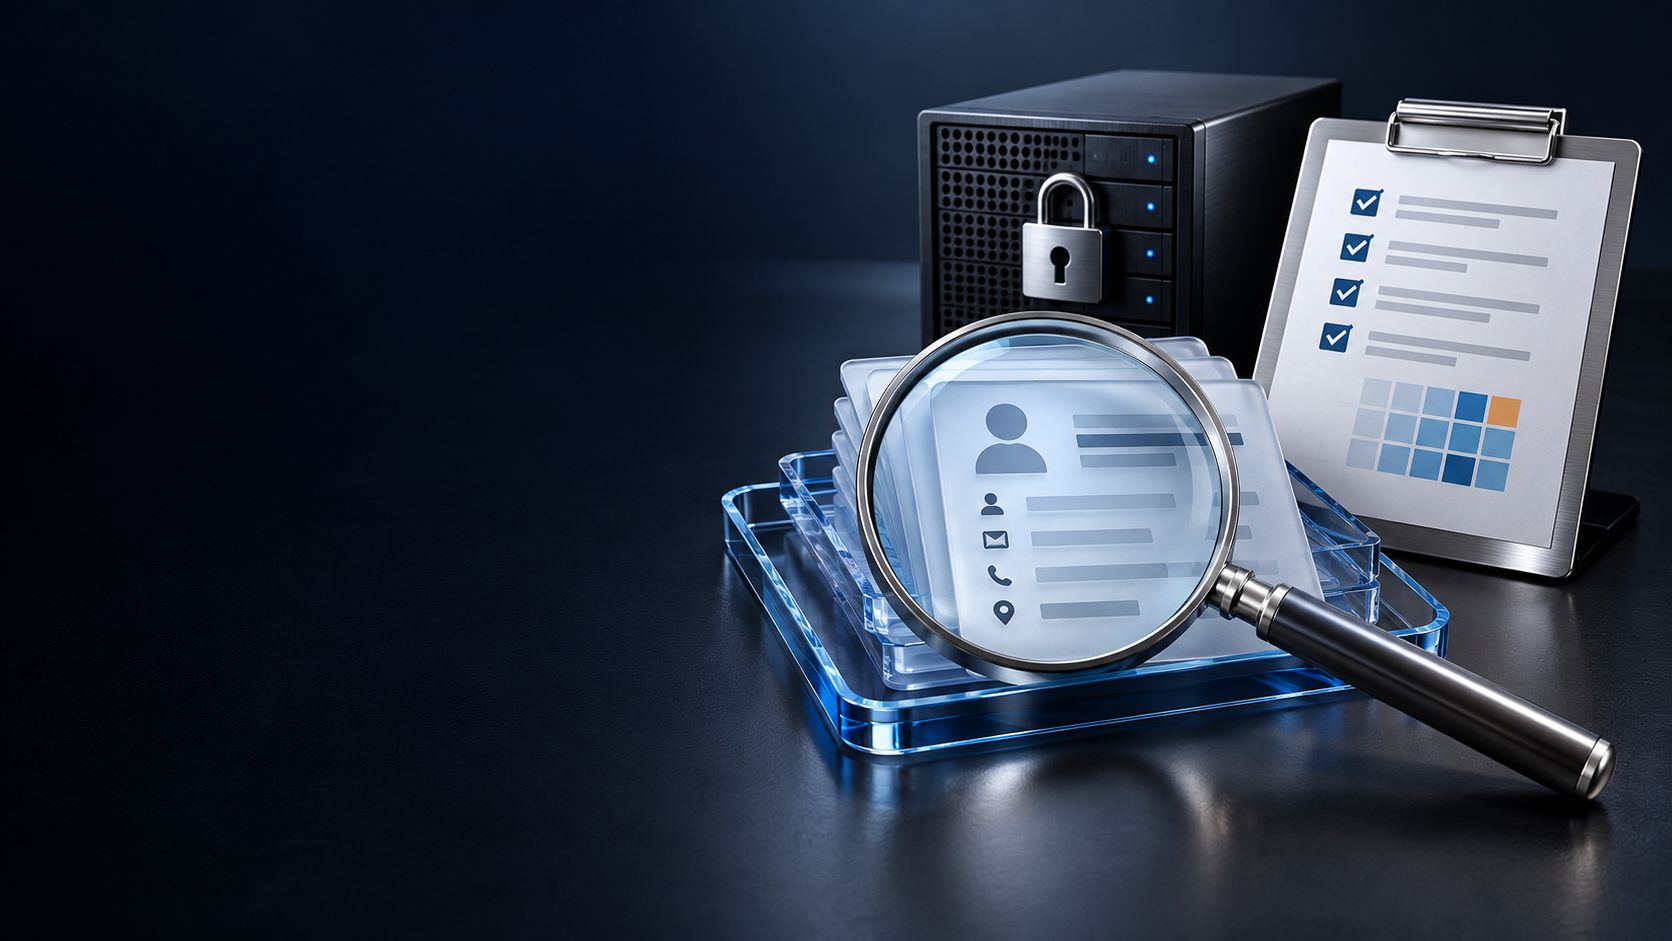
Structured assessment of privacy risk for new systems, vendors and processing activities before they go live.
New products, analytics, AI use and vendor tools often change how personal data is used.
New products, analytics, AI use and vendor tools often change how personal data is used. A privacy impact assessment finds the risks while changes are still cheap to make, and records the reasoning for regulators, customers and your own board.
What the engagement covers
- Screening to decide which projects need a full assessment
- Description of the processing: purpose, data, people affected, flows and retention
- Necessity and proportionality review
- Identification and rating of privacy risks to individuals
- Controls and safeguards to reduce each risk
- Transfer impact review where data leaves its home jurisdiction
- Residual risk sign-off and review triggers
- Reusable templates and a lightweight assessment process for your teams
Understand. Prioritize. Enable.
How we deliver privacy impact assessment, step by step.
- 01
Screen
Quick triage to see which activities need a full assessment and which can proceed with standard controls.
- 02
Describe and analyse
We document the processing and test it against purpose, necessity and the requirements that apply to you, including the PDPL, the GDPR or any other law that applies to you.
- 03
Reduce the risk
Practical safeguards are agreed with the project owners and recorded with clear accountability.
- 04
Record and review
A decision record, residual risk sign-off and a trigger for reassessment when the processing changes.